The complete archive — filter by area, or browse the full list.
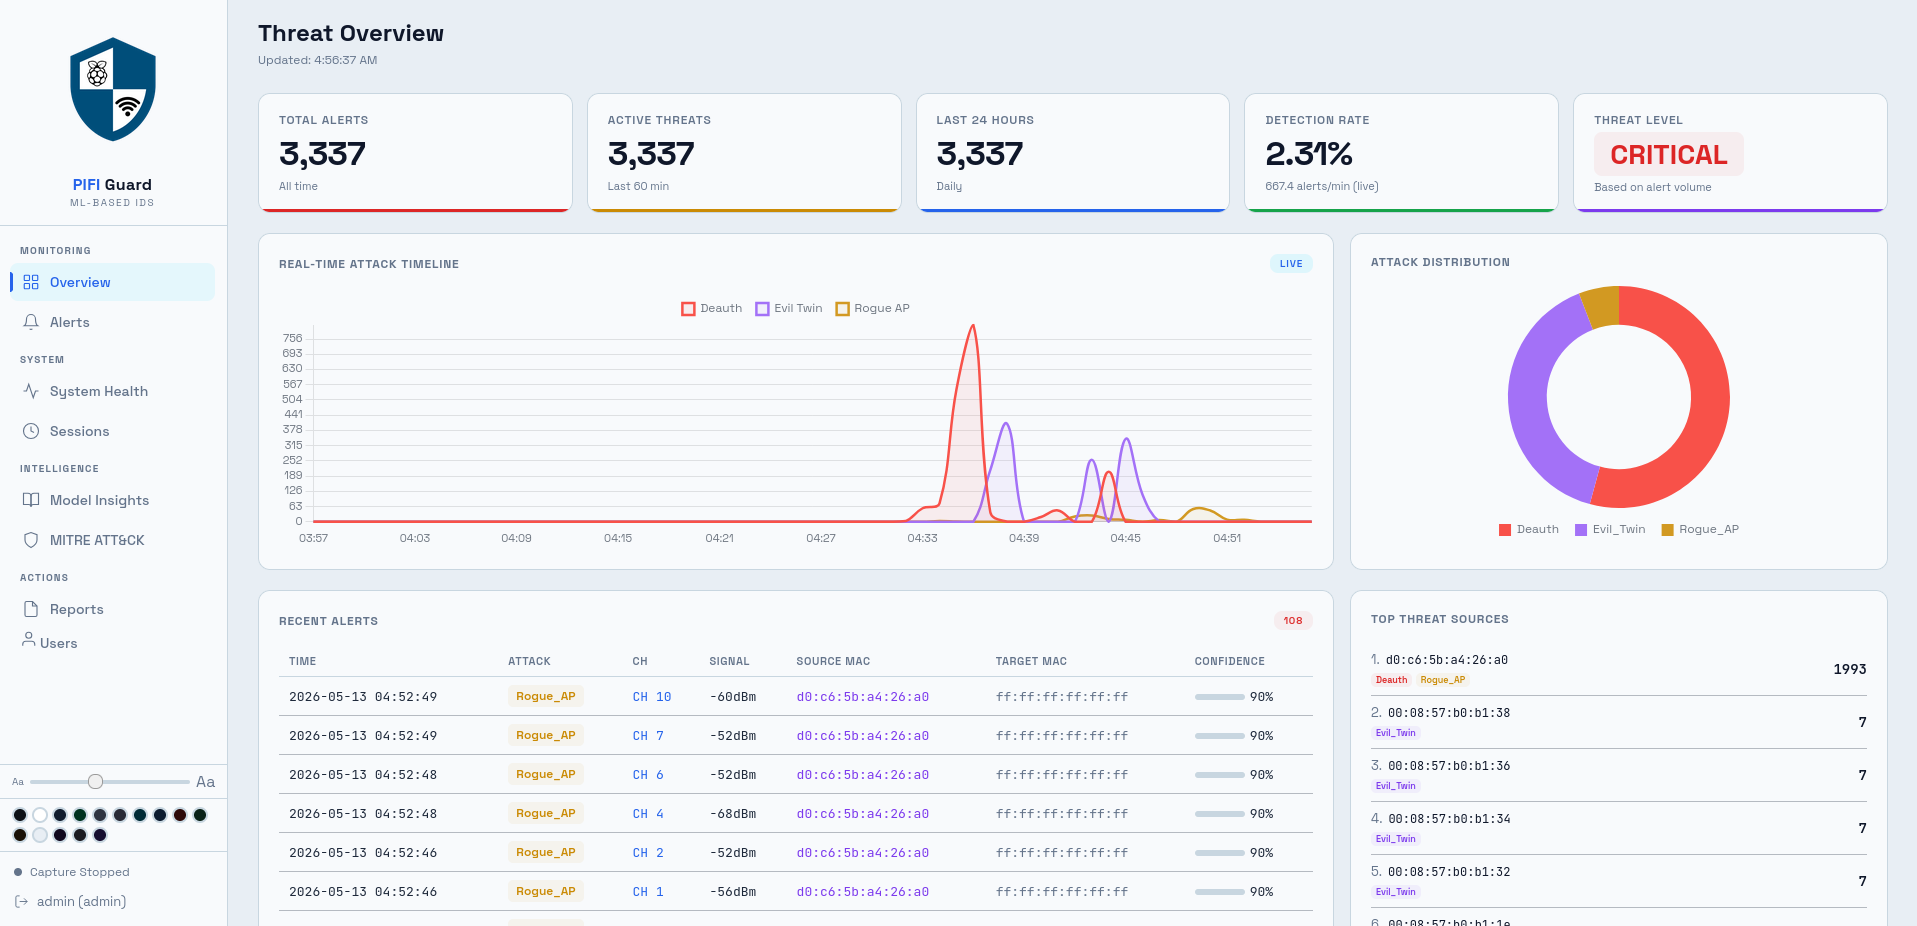
PIFI Guard — ML Based IDS For Public WIFI
ML-based Intrusion Detection System for Public Wi-Fi Security. Detects Evil Twin, Deauthentication, and Rogue AP attacks with zero false positives.
PythonRaspberry PiMITRE ATT&CKExplainable AI
Read on LinkedIn
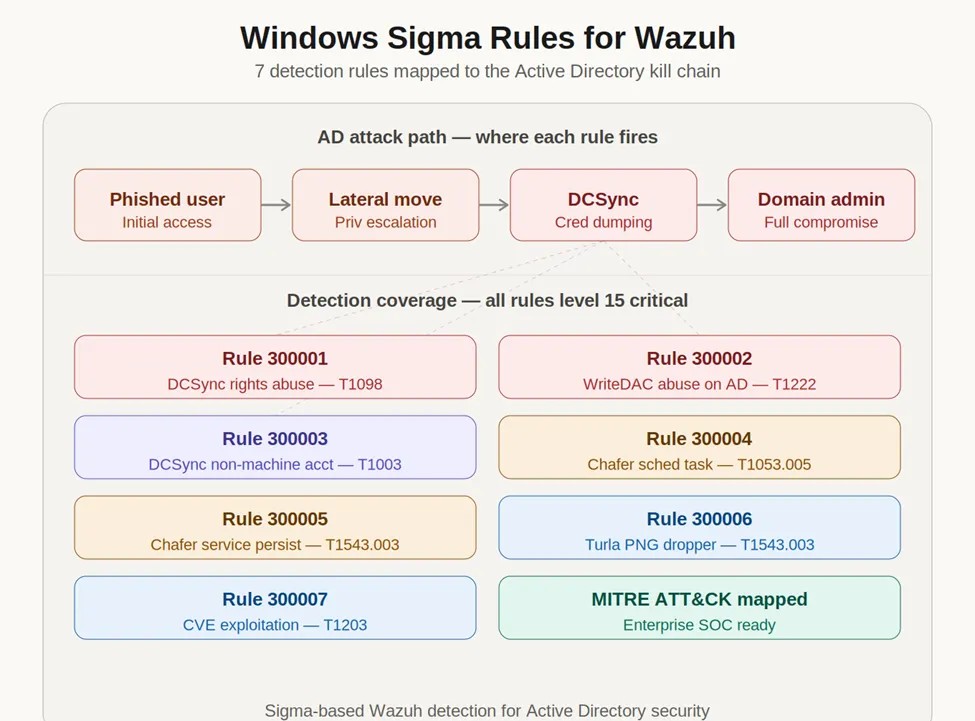
Windows Sigma Rules
Developed Sigma-based Wazuh rules to detect Active Directory attacks, privilege escalation, DCSync, persistence, and post-exploitation activity. Enabled advanced threat detection and threat hunting through Windows event log analysis.
SigmaWindowsThreat HuntingDetection
Read on Medium
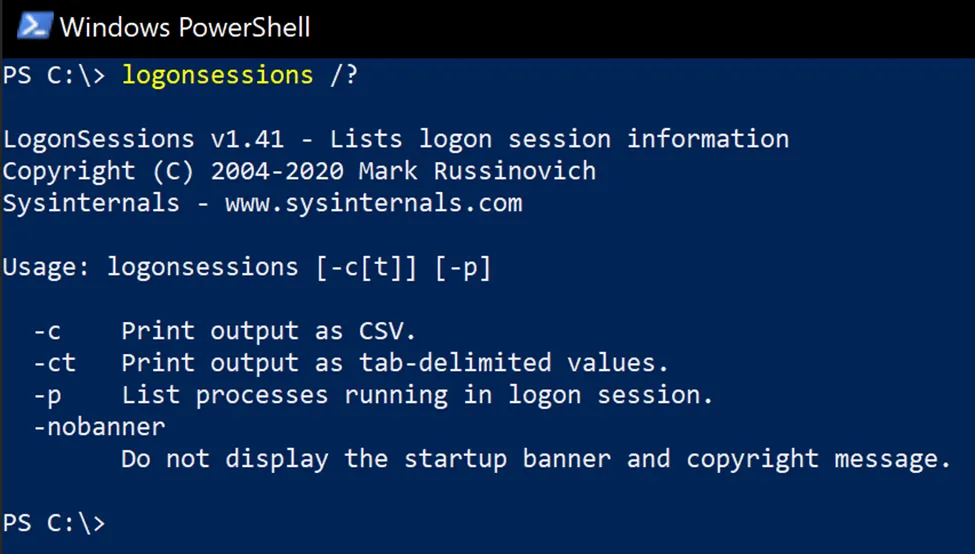
Sysinternals — Logonsessions Custom Rule
Developed a Wazuh correlation rule using Sysinternals Logonsessions to detect suspicious logon sessions followed by PowerShell, PsExec, or RDP activity. Triggers critical alerts by correlating high-risk user sessions and post-logon behavior.
WazuhSysinternalsMITRE T1078Detection
Read on Medium
Custom Wazuh Rules for PowerShell
Developed custom Wazuh rules to detect malicious PowerShell commands, in-memory stagers, and suspicious script execution. Enhanced detection of execution, lateral movement, and post-exploitation activity on Windows systems.
PowerShellWazuhDetectionWindows
Read on Medium
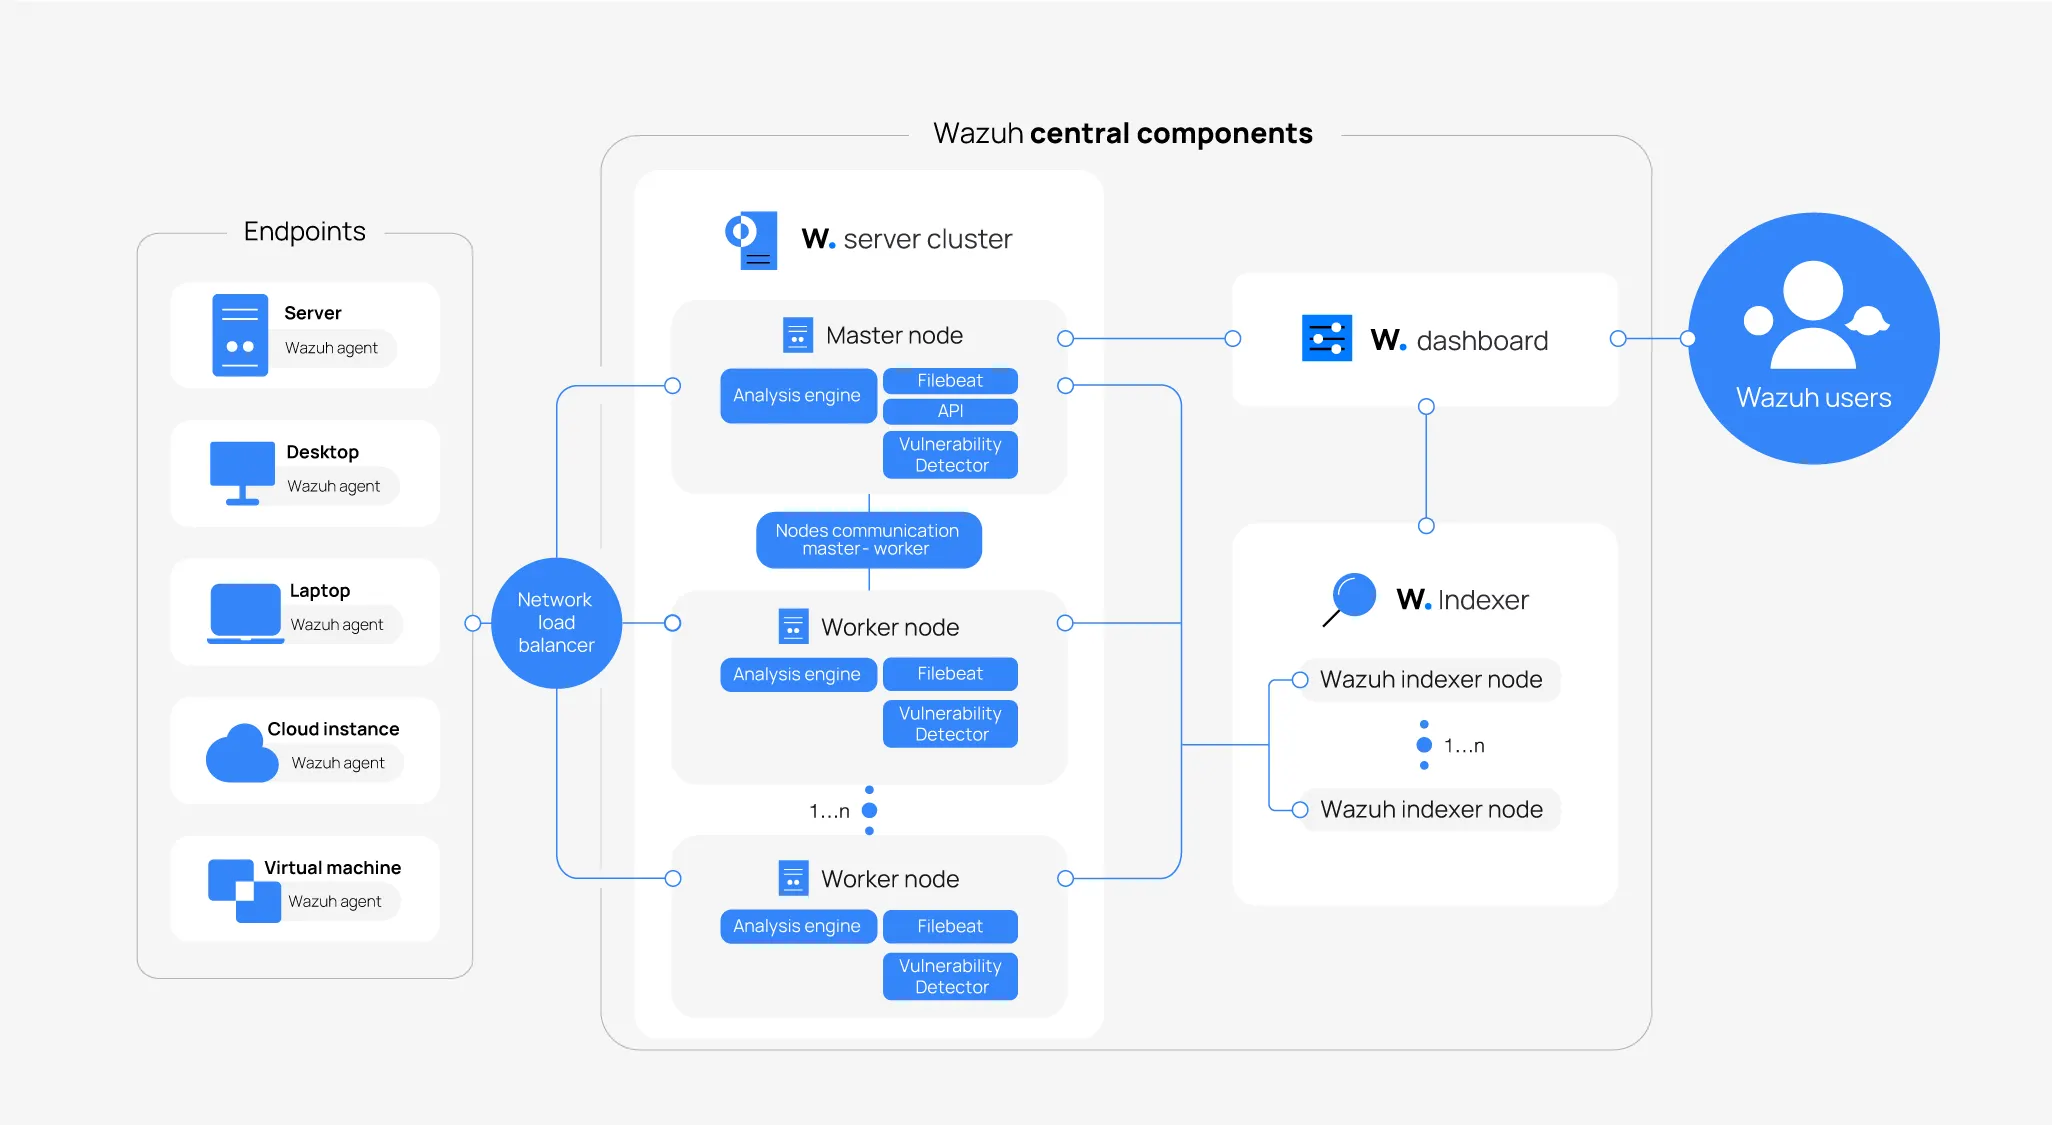
High Availability Wazuh Cluster
Deployed a high-availability Wazuh cluster (Version 4.12.0) for robust log monitoring, analysis, and enterprise-grade security operations.
WazuhHALog MonitoringSIEM
Read on Medium
Secure SMB Backup for Wazuh
Configured secure Samba (SMB) backup solutions for Wazuh and OpenSearch snapshots, ensuring data integrity and disaster recovery.
SMBWazuhOpenSearchBackup
Read on Medium
Snapshot & Restore Configuration
Implemented snapshot and restore configuration for Wazuh/OpenSearch, enabling efficient data backup, migration, and recovery strategies.
WazuhOpenSearchSnapshotDR
Read on LinkedIn
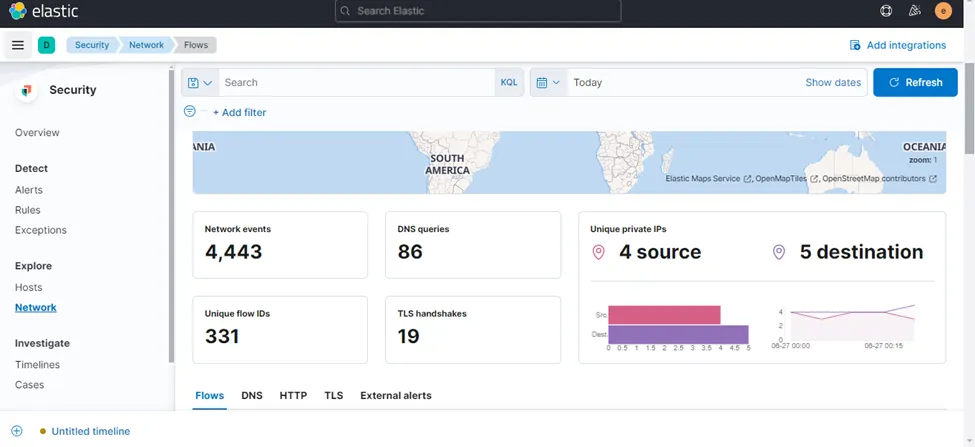
SIEM: Suricata + Elastic Stack
Installed and configured Suricata IDS with Elastic Stack on Ubuntu for comprehensive security monitoring and threat detection.
SuricataElastic StackSIEMUbuntu
Read on Medium
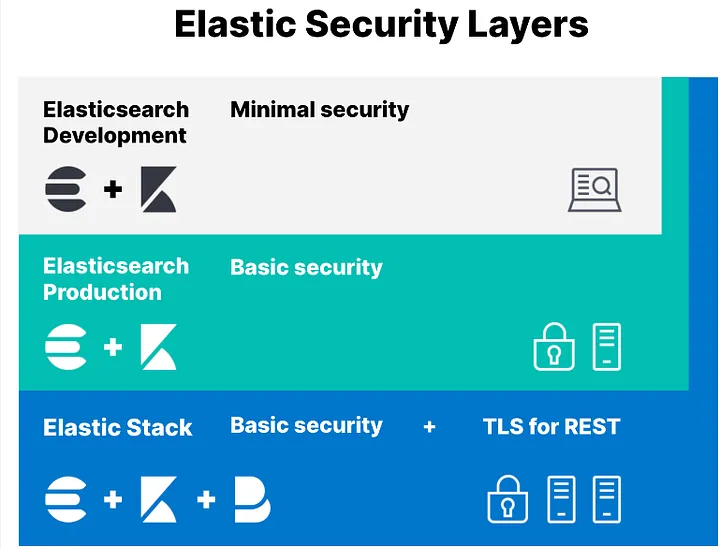
TLS Security for Elasticsearch & Kibana
Advanced TLS security implementation for Elasticsearch and Kibana, securing communication between SIEM components.
TLSElasticsearchKibanaSecurity
Read on Medium
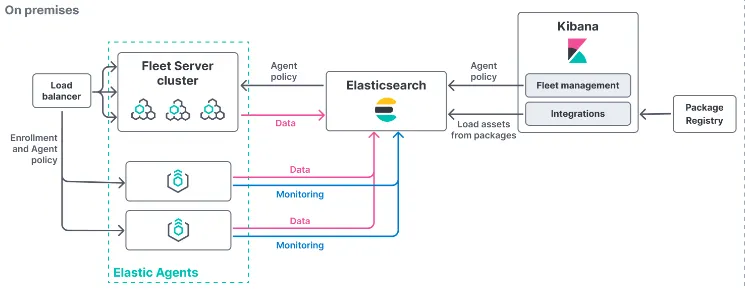
Fleet Server Deployment On-Premises
Deployed Fleet Server on-premises for centralized agent management and monitoring. Enabled secure, scalable operations across distributed and private network environments.
FleetAgentMonitoringOn-Prem
Read on Medium
Android Hacking with Metasploit
Demonstrated remote Android exploitation using Kali Linux and Metasploit-Framework, creating payloads with msfvenom and configuring listeners.
MetasploitAndroidKaliRed Team
Read on Medium
Snort As an Intrusion Detection System
Configured Snort for effective intrusion detection and demonstrated exploitation techniques for SMB EternalBlue and Log4j vulnerabilities.
SnortIDSEternalBlueLog4j
Read on LinkedIn
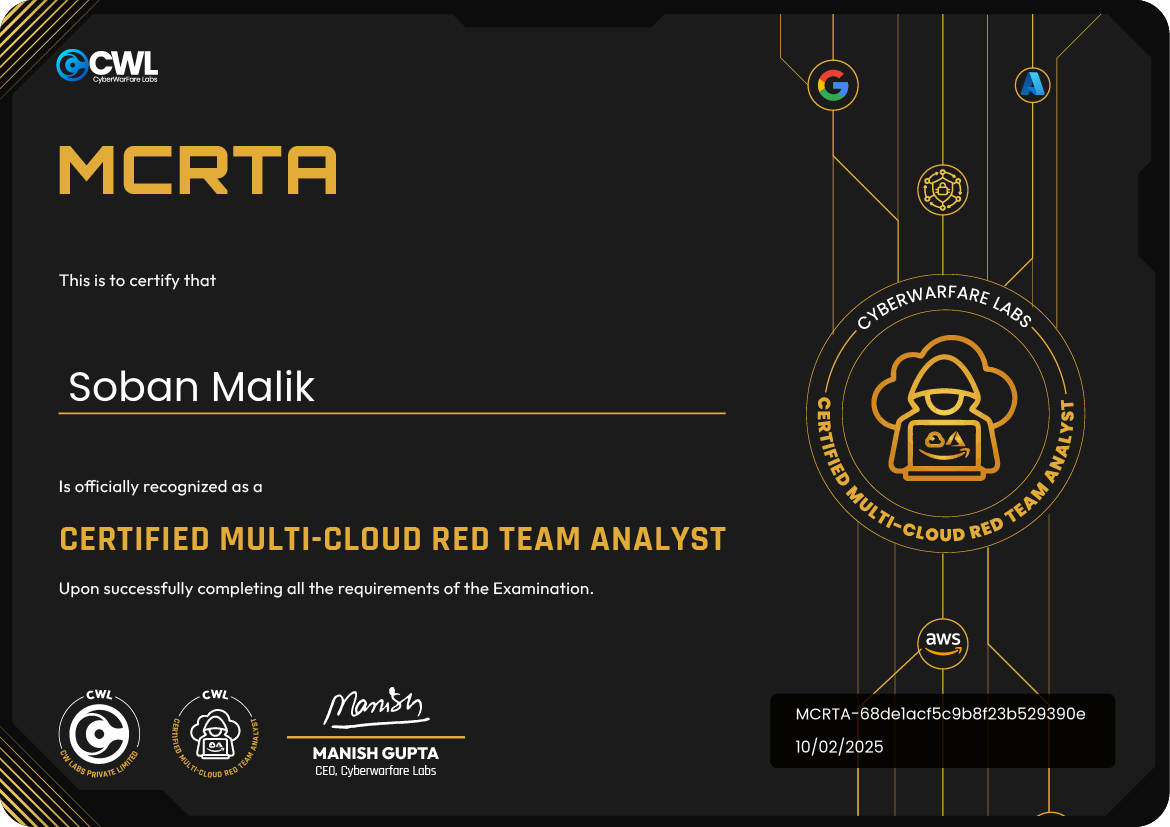
MCRTA — Multi-Cloud Red Team Analyst
Earned MCRTA certification from CyberWarFare Labs, gaining practical experience in Cloud Adversary Simulation, MITRE Cloud ATT&CK, and AWS/Azure/GCP security. Developed practical skills in IAM, RBAC, cloud red teaming, and enterprise cloud security operations.
AWSAzureGCPRed Team
Read on LinkedIn
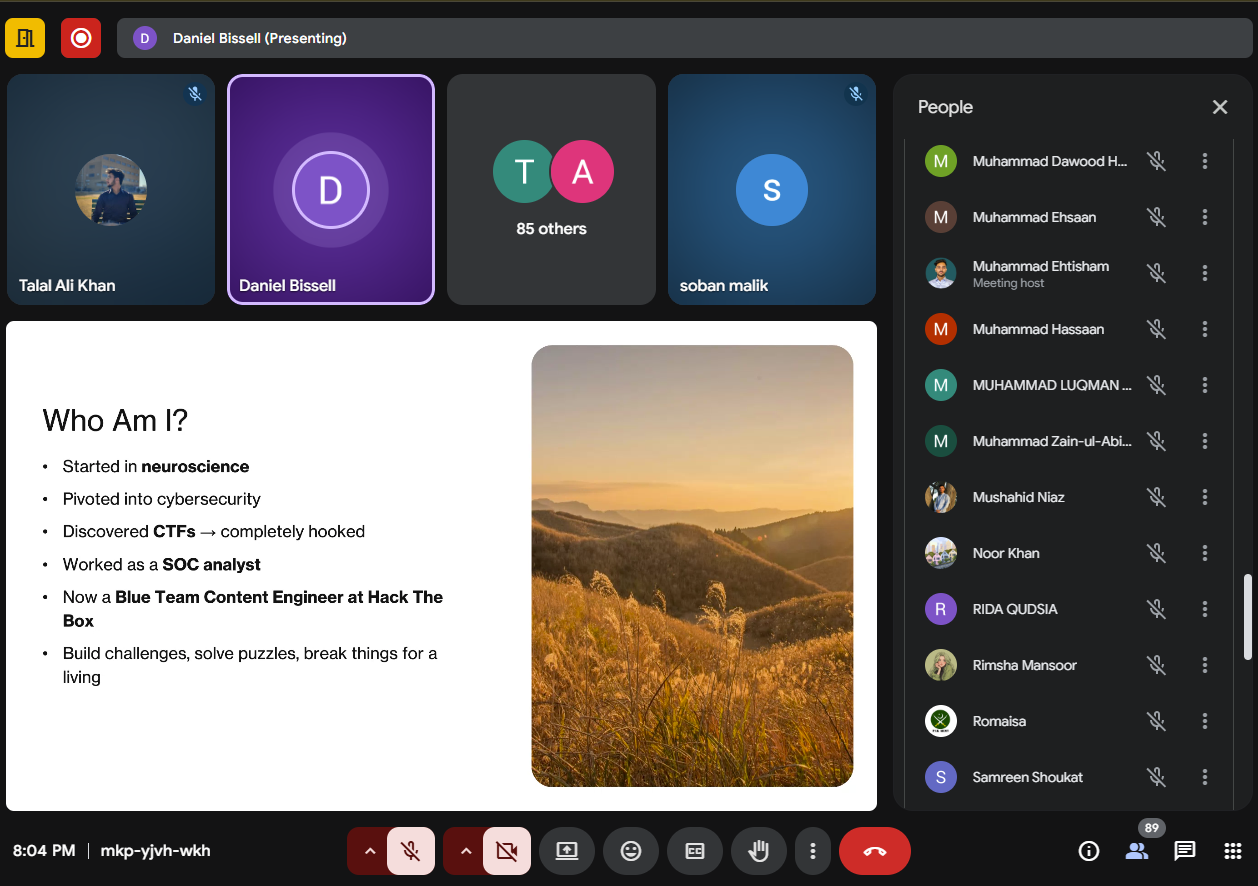
Capture The Flag (CTF) Training — Air University
Organized and conducted a Capture The Flag (CTF) at Air University introducing students to OSINT, Forensics, Web, Crypto, Reverse Engineering, and Pwn challenges. Guided participants on CTF methodologies, tools, career pathways, and cybersecurity skills development.
CTFTrainingOSINTForensics
Read on LinkedIn
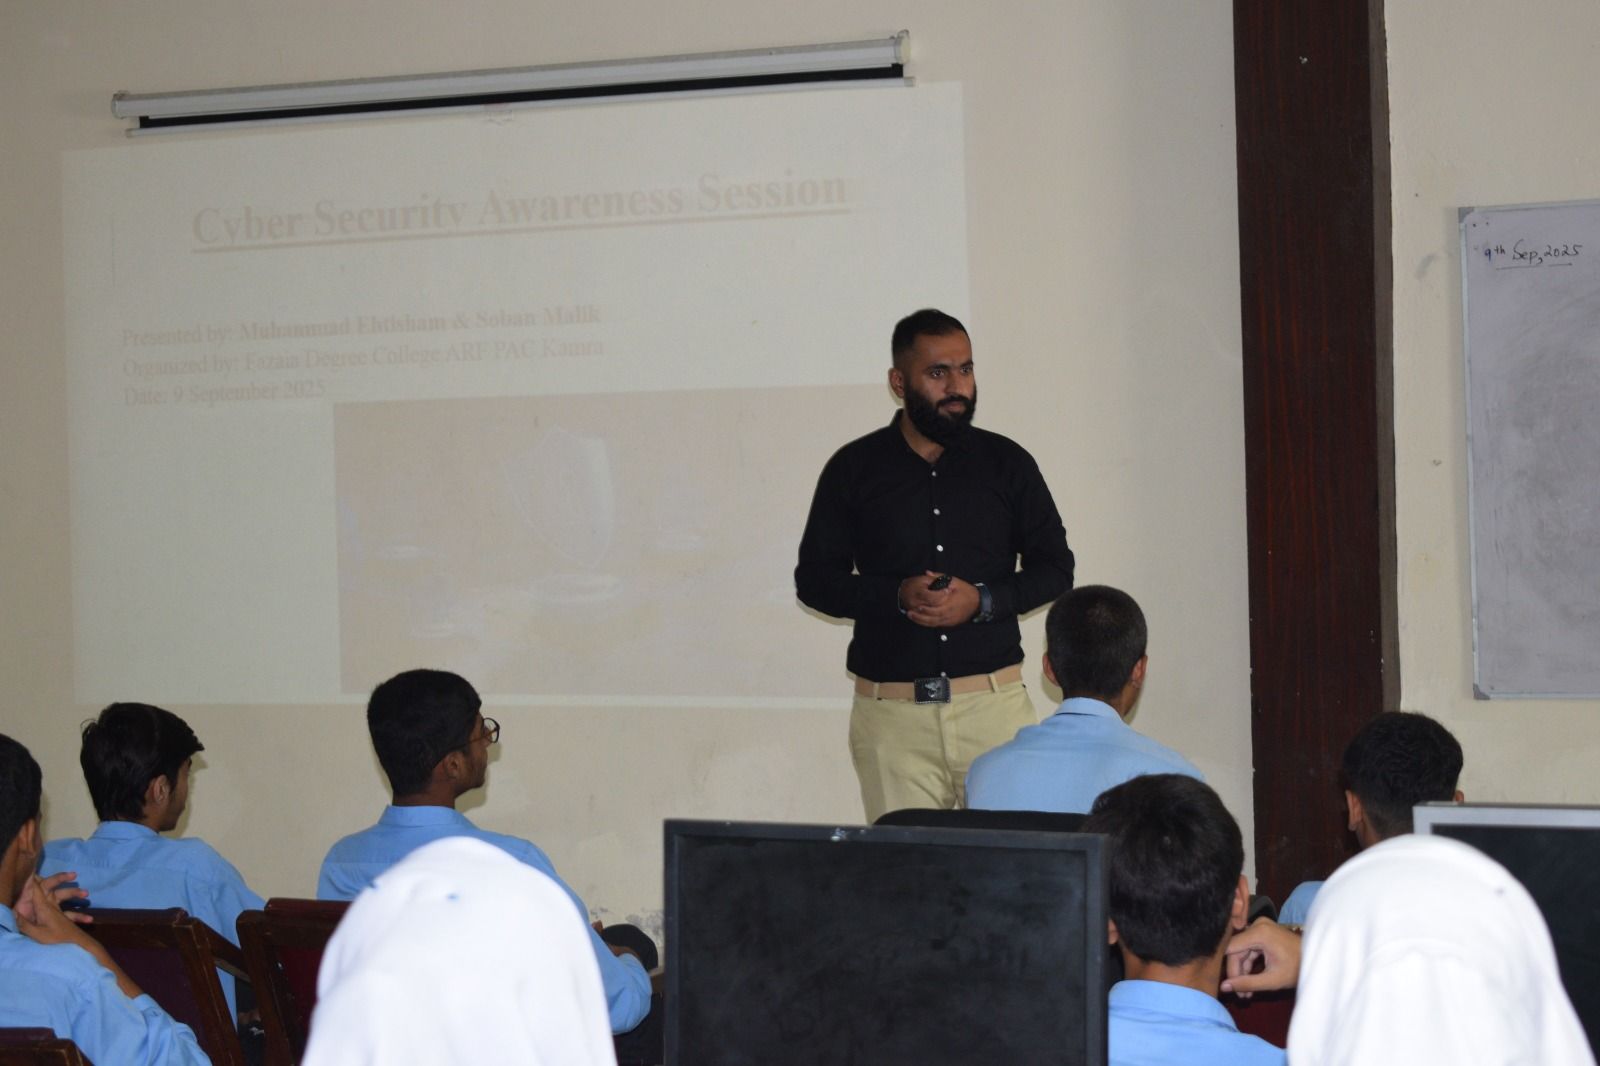
Cyber Security Awareness Sessions
Conducted multiple awareness sessions at GCT Attock and Fazaia Degree College And Comsat Attock, covering AI & Deepfakes, Cyber Crimes, Social Engineering, and Wi-Fi Security.
AwarenessTrainingSocial EngineeringWi-Fi
Read on LinkedIn
Web App Security Assessment (Part 1)
Performed comprehensive web application security assessment using OWASP Juice Shop and OWASP ZAP. Identified XSS, SQL Injection, DOM-Based XSS and Broken Authentication.
OWASPZAPJuice ShopVAPT
Read on Medium
Web App Security Assessment (Part 2)
Advanced web application security assessment continued from Part 1. Deep-dive into exploitation techniques, Broken Access Control, Directory Traversal and Cross-Site Request Forgery (CSRF).
OWASPZAPExploitationRemediation
Read on Medium
DryFoods Hub — Secure E-commerce
Secure e-commerce marketplace built with OWASP Top 10-aligned security practices including CSP, CSRF protection, HSTS, and comprehensive input validation.
OWASPSecure CodingHSTSCSP
Visit Site
Distributed Chat System with Offensive Content Monitoring
Real-time distributed messaging system with offensive content detection, multi-language support, logging, and multi-threading for simultaneous clients.
DistributedModerationMulti-ThreadingLoggingPlatform Independence
Read on LinkedIn
Basic Shell Scripting (Ubuntu)
Learned and implemented shell scripting fundamentals on Ubuntu, enabling automation and efficient system administration.
BashUbuntuAutomationSysAdmin
Read on Medium
Using Logs to Track Issues in Linux
Demonstrated how to use Linux logs for efficient issue tracking and troubleshooting, enabling swift problem resolution.
LogsLinuxTroubleshootingSysAdmin
Read on Medium
Using Logs to Track Issues in Windows
Continuous monitoring of Windows logs using Event Viewer for security events detection and rapid issue resolution.
Event ViewerWindowsLogsMonitoring
Read on Medium
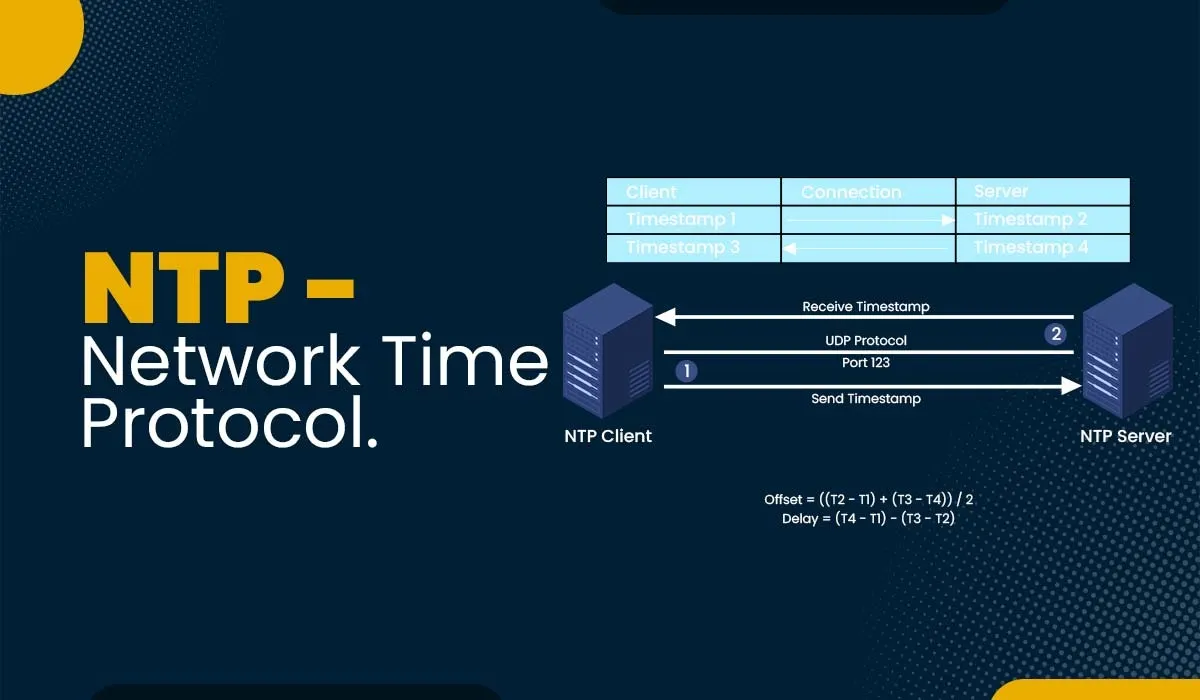
Install & Configure NTP on Linux
Set up NTP server and client for synchronized time management across Linux systems, essential for logging and authentication.
NTPLinuxSynchronizationTime
Read on Medium
Configure UFW Firewall in Kali Linux
Configured Uncomplicated Firewall (UFW) in Kali Linux for network security, securing systems with simple yet effective firewall rules.
UFWKaliFirewallSecurity
Read on Medium
Online Bookstore Database Schema
Designed a robust database schema for an Online Bookstore managing customers, books, orders, and inventory with scalability and data integrity.
MySQLDatabase DesignERDNormalization
Read on Medium
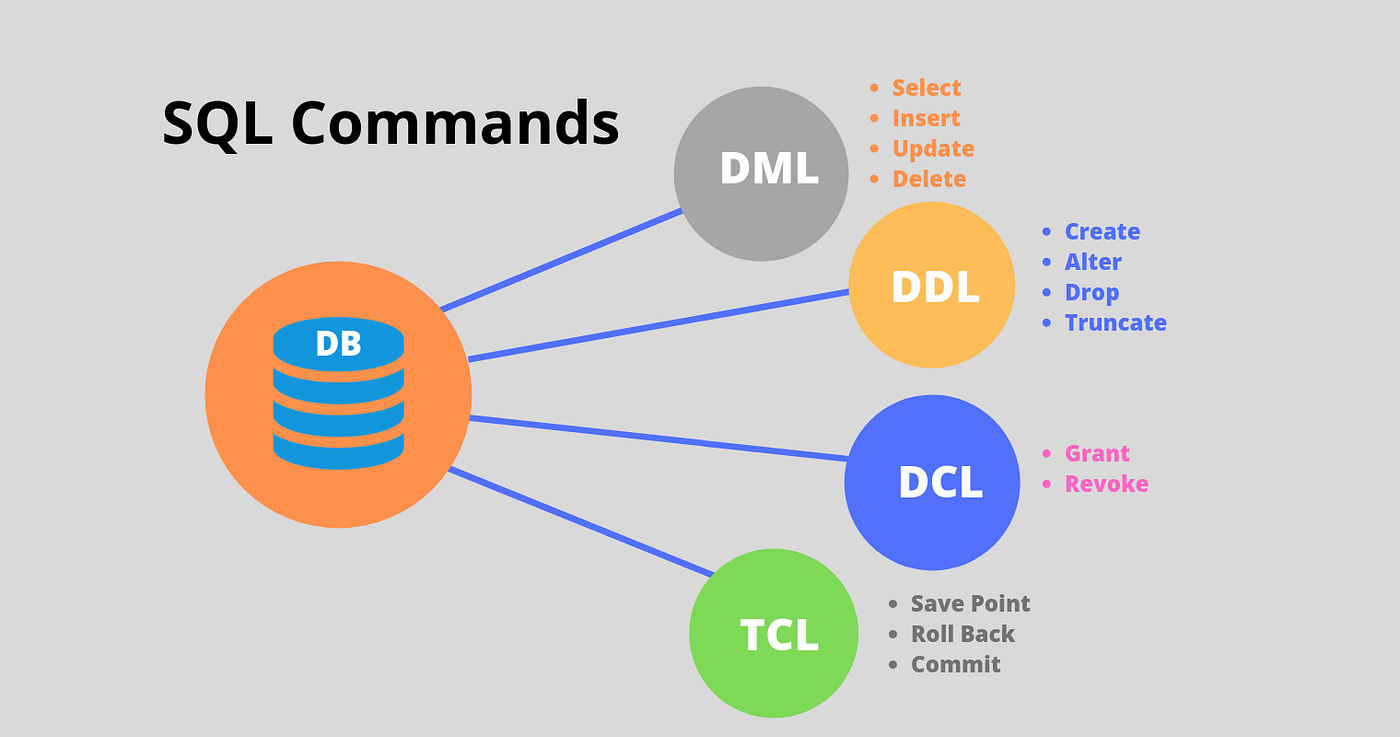
DDL Commands & Database Design
Explored Data Definition Language (DDL) and basic SQL commands, gaining insights into creating, modifying, and managing database structures.
DDLSQLDatabaseDesign
Read on Medium
Install MySQL & MySQL Workbench
Step-by-step guide to installing and configuring MySQL and MySQL Workbench on Windows for database development and administration.
MySQLWorkbenchWindowsInstallation
Read on Medium
Partition & Format Disk in Windows
Efficient disk management guide covering how to seamlessly partition and format disk drives in Windows for enhanced data organization.
WindowsDisk ManagementPartitionFormat
Read on Medium